This guide explains how to interpret Pi9691133599, umefra189, and related identifiers for consistent procurement and safe deployment. It then provides objective background on why structured part or lot codes matter, how suppliers document specifications, and what due diligence looks like—without relying on unverifiable claims.
If you encounter Pi9691133599 alongside umefra189 (and similar alphanumeric identifiers), treat them as structured references that must be verified against documented specifications before purchase, integration, or operational use. The most reliable outcomes come from aligning the identifier with the correct technical sheet, material/compatibility requirements, and the supplier’s traceability records.
In practical terms, the goal is simple: ensure that the item you receive corresponds to the exact identity implied by codes like Pi9691133599 and umefra189. For many industries, that verification step reduces downstream risks such as mismatched tolerances, incorrect interfaces, incompatible materials, and documentation gaps during audits.
What makes these codes particularly important is that they often function as “short handles” for long and strict sets of requirements. A part number or identifier is rarely just a label; it is frequently the key that selects a specific configuration, a specific revision state, and a specific documented proof trail. If those assumptions are wrong, even by a small margin, the mismatch can surface late—during commissioning, acceptance testing, warranty performance checks, reliability testing, or regulatory audits. Therefore, good practice is to treat these identifiers as promises from the supplier that must be validated by paperwork and evidence.
To be clear, this does not mean every identifier requires a full engineering redesign or deep forensic investigation. It means you should follow a consistent method to confirm that the identifier maps to the same requirements your project expects. The verification process can be lightweight when documentation is clean and revision control is straightforward, but it should be deliberate enough to avoid “assumptive matching,” where teams assume that the visual appearance, description, or generic category is sufficient.
Identifiers such as Pi9691133599 and umefra189 often function as compact keys inside larger information systems. They may map to a specific bill of materials entry, a lot/serialization scheme, an approved drawing package, or a quality-control checkpoint. Even when two items appear visually similar, the identifier can correspond to different revision states, manufacturing runs, or compliance constraints.
From an expert procurement and quality perspective, the safest workflow is to avoid “assumptive matching.” Instead, confirm the identifier against:
To understand why this matters, consider how organizations actually run. Most technical enterprises depend on controlled documents and controlled change processes. A part number often ties into a revision-controlled drawing. That drawing ties into specific manufacturing instructions. Those instructions tie into work instructions, tooling setups, and inspection plans. Those plans tie into records that prove what was made and how it was verified. Finally, customers (or internal engineering teams) use the identifier to decide how to inspect upon receipt, how to accept the product, and how to troubleshoot if the delivered piece fails a test.
When procurement bypasses verification, it introduces uncertainty right into the heart of the quality chain. Teams can lose time because they need to perform emergency re-inspection, re-document compliance, request revised certificates, or (in the worst cases) scrap material or redo installations. In regulated contexts, that can also create audit exposure. Auditors typically look for traceability from purchased item to acceptance record to controlled specification. If Pi9691133599 and umefra189 are not properly mapped, you may be unable to demonstrate that link.
It is also common for suppliers to re-use codes across categories or to create sub-variants under the same umbrella model. For example, two products might share a base description but differ in plating thickness, heat treatment, insulation rating, software configuration, packaging cleanliness class, or measured performance thresholds. Without revision and configuration verification, “same category” quickly becomes “not actually the same.”
Therefore, in professional practice, identifiers matter because they reduce ambiguity. They are supposed to convert an uncontrolled real-world item into a controlled reference. Your job (as buyer, integrator, or QA approver) is to ensure that conversion happens correctly.
Because the keywords provided do not include an explicit product category, it is best to interpret them as codes rather than as standalone descriptions. In other words, Pi9691133599 and umefra189 should be treated as references that require verification—similar to how a part number or internal SKU must be checked for configuration details.
An objective way to proceed:
One effective approach is to interpret identifiers as identifying metadata. They rarely carry enough information by themselves to guarantee correctness; rather, they reference something else. That something else is usually a technical document, a configuration database entry, or a controlled manufacturing/inspection program. When you treat the code as metadata, you naturally design your process around verification and evidence.
To make this less abstract, consider how teams interact with suppliers. Most procurement processes revolve around the ability to answer questions like: “What exactly did you build?” and “How did you verify it?” The best suppliers can provide a clean audit trail connecting a code to a build record and inspection results. A less reliable supplier might only provide a general description (“this should be fine,” “it’s the standard version,” or “it’s functionally equivalent”). In those cases, you should be cautious, because “functionally equivalent” is frequently a loophole that hides differences in documented acceptance criteria.
An objective interpretation also requires resisting the temptation to infer meaning based on the code’s appearance. For example, a buyer might assume that “Pi9691133599” is some kind of model number and that “umefra189” is an internal vendor code or variant code. While those assumptions could be correct, objective practice means you cannot rely on guessing. You must determine meaning by referencing supplier documentation or internal crosswalks.
In short: treat Pi9691133599 and umefra189 as keys that unlock verified information. Do not treat them as the verified information themselves.
You asked for price information to be integrated; however, the prompt does not provide a specific price, currency, or pricing table. In such cases, industry best practice is to avoid guessing. Instead, you should request a formal quote and reconcile it with the technical identity of Pi9691133599 and umefra189.
In procurement reality, pricing often varies because the identifier may correspond to:
If you are comparing supplier offers, compare apples to apples: the quote line item should explicitly reference the relevant identifiers (e.g., Pi9691133599 and umefra189) and include documentation terms (inspection, certificate of conformity, traceability pack) that match your requirements.
More detailed procurement guidance often includes structuring your request for quote (RFQ) so that price comparisons remain meaningful. If your RFQ includes only a textual description, suppliers can interpret it differently. If your RFQ includes the exact identifiers plus required documentation deliverables, you create a common basis for quoting.
For example, you can include in your RFQ:
When the quote line items explicitly tie to Pi9691133599 and umefra189, it becomes easier to evaluate price differences fairly. A supplier quoting lower cost may be excluding traceability documentation, substituting a revision, or compressing inspection scope. Those cost differences can show up as hidden costs later (rework, delays, audit issues, or failures).
From a risk-management angle, it can be helpful to separate cost into components: unit price, documentation fee, inspection fee, packaging/handling fee, and logistics lead time. Not every invoice line will be labeled this way, but a disciplined RFQ encourages transparent breakdowns. That transparency is often as important as the unit price itself, because quality assurance deliverables are frequently part of the true total cost.
Therefore, absent exact numeric data, the best procurement recommendation is to treat pricing as a negotiated result of identifier correctness and documentation scope, not as an assumed fixed figure associated with the codes alone.
When dealing with structured codes like Pi9691133599, a supplier’s credibility is not only about delivery—it is about whether their documentation trail is usable in your operational and compliance context.
Key verification points typically include:
Supplier due diligence should also consider responsiveness and clarity. A supplier who can provide mapping quickly and consistently—without vague language—tends to have mature configuration management. Configuration management maturity matters because identifier systems can only be trusted when revisions and build records are controlled. If the supplier’s documentation is inconsistent, outdated, or missing revision references, then the code becomes less trustworthy.
It’s also useful to check whether the supplier can produce the evidence you need before shipment, not only after. For some industries, advanced evidence (like pre-shipment sample inspection results or certificate draft copies) reduces the likelihood of last-minute surprises. Even when not feasible, the supplier should state what they will provide and when they will provide it.
Another common due diligence checkpoint is the supplier’s labeling and packaging practices. Traceability is not only an internal database concept; it also depends on whether the physical item and packaging labeling match the documented identifiers. If the supplier’s box label lists an identifier but the certificate maps to a different batch, you have a mismatch that undermines traceability. Therefore, verify that labeling conventions align with the certificate of conformity and the lot/serial record.
Additionally, investigate whether the supplier’s quality system supports identification retention. If a supplier cannot retain or retrieve inspection records tied to Pi9691133599 and umefra189 within the retention period you require, it can be a problem later. Some organizations also require defined record retention times for regulatory compliance and customer support obligations.
Finally, pay attention to nonconformance management. If the delivered items do not meet requirements, do they have a structured process to issue nonconformance reports, propose corrective actions, and handle replacements or rework? The ability to respond to issues is often the real proof of supplier capability, not just their initial paperwork.
Even if Pi9691133599 and umefra189 are correct, integration still requires attention to application conditions. Depending on the domain (industrial components, electronics, manufacturing consumables, or other technical items), the following checks are often essential:
Because these keywords do not specify a location term or application domain, you should treat the above as general conditions and refine them based on your internal engineering or QA requirements.
In integration, there’s a specific risk pattern: even correct items can fail if installation conditions differ from what the specifications assumed. For example, some components require controlled cleanliness levels at install. Others require specific torque values or torque-angle methods. Some require preheating or controlled thermal ramp rates. Others have limits on exposure duration to humidity (e.g., moisture-sensitive devices). If a team installs the item correctly but under different environmental conditions, performance might degrade or the item might fail functional or reliability tests.
Integration checks should therefore connect the identifier’s documented requirements to your practical operational plan. That means your engineering team should review the supplier’s spec pack and confirm how it translates to your installation procedures and acceptance criteria.
Also consider compatibility at the system boundary. Sometimes the identifier corresponds to a mechanical part, but the system boundary might include an interface like a connector, a harness, a coupling, a software setting, or a calibration constant. Even if the physical part is correct, mismatched mating components or mismatched interface standards can cause failure. A disciplined approach ensures that your interface library (your internal set of accepted mating geometries or electrical standards) agrees with the supplier’s interface definitions.
Additionally, operational acceptance should include verification beyond paperwork. Paperwork verifies identity and traceability; it does not always prove that the delivered item will pass your functional tests under your specific system configuration. Therefore, incoming inspection and test plans should be risk-based: test what matters most to your use-case.
For some organizations, a best practice is to define critical-to-quality (CTQ) characteristics and ensure that they align with what the supplier measures and what you measure upon receipt. If the supplier’s inspection scope is weaker than your application risk profile, you might need supplementary tests. Conversely, if your tests are redundant, you can optimize to reduce unnecessary cost. The key point is that CTQ alignment is easier when the identifier mapping is correct.
| Area | What to Check | Typical Evidence to Request |
|---|---|---|
| Identifier mapping | How Pi9691133599 and umefra189 map to a drawing, revision, or approved configuration | Specification crosswalk, revision-controlled datasheet, document index |
| Traceability | Whether the supplier can link the identifier to production lots and inspection records | Batch/lot traceability report, certificate of conformity, inspection records |
| Compatibility | Whether the identifier matches your interface and acceptance criteria | Compatibility matrix, installation guidance, acceptance test criteria |
| Quality requirements | Whether incoming inspection aligns with your risk profile | Incoming QA checklist, sampling plan, nonconformance procedure |
| Change control | How revisions are handled and whether substitutions are equivalent | Change notice, equivalency statement, revision history log |
Even though this table uses general categories, the workflow it implies is highly repeatable. Once you establish a mapping for Pi9691133599 and umefra189, you can standardize incoming inspection criteria around that mapping. This reduces cognitive load for procurement and QA teams, because the same verification checklist can be reused for future orders that reference the same identifiers.
Over time, organizations often create internal “identifier dossiers” that contain: supplier mappings, internal acceptance test procedures, and a record of prior lot performance. Those dossiers effectively become a knowledge base. When issues occur, teams can quickly narrow down whether the problem is related to revision differences, a specific lot, or a broader supplier process change.
The key is that the identifier-to-document mapping is the foundation that makes the internal dossiers reliable.
Use the following approach when you receive Pi9691133599 and umefra189 in a quote, inquiry, or technical document. This sequence is designed to reduce integration and acceptance risk.
Because the code names provided do not include an explicit technical domain, it’s important to translate the steps into your industry context. Here are examples of how these steps might be adapted in different domains:
In each scenario, the key is the same: the identifier points to documented truth, and your procurement/QA process should follow that truth. If you find conflicts—such as a quote stating Pi9691133599 but a certificate referencing a different revision—stop and resolve the discrepancy before installation. The cost of resolving identity issues during procurement is usually far lower than resolving them after the system fails a test or reaches end-use.
To operationalize the identifiers safely, establish internal conditions that prevent common procurement errors. These are generic requirements you can adapt to your organization:
Internal requirements can become even more powerful when they are turned into enforcement mechanisms. For instance:
Many organizations also define a “stop ship” or “stop use” policy tied to documentation mismatches. For example, if Pi9691133599 does not match the certificate identifiers, or if umefra189 cannot be mapped to the expected revision-controlled document set, the item is held for resolution. This policy reduces the chance that someone will install a part before identity has been verified.
Another useful internal requirement is to define what constitutes equivalency. If a supplier proposes a substitution, internal policy should require documented equivalency evidence. Equivalency should not be based solely on functional similarity; it should be based on matched specifications, matched revision states (or explicitly approved changes), and consistent traceability. If equivalency changes a critical parameter, it should trigger an engineering approval step.
Finally, ensure internal record-keeping practices align with audit needs. If you will be inspected later, you need a consistent way to retrieve: which suppliers shipped what, which lot or serial was received, which documentation was provided, and which acceptance tests were performed. Identifier-centric record-keeping makes this significantly easier.
In many technical sectors, the shift toward structured part numbering and traceability systems reflects a broader industry need: accountability across the lifecycle. When an organization can connect a code like Pi9691133599 to defined specifications and production/inspection evidence, it becomes easier to manage quality, prevent mix-ups, and respond to corrective actions.
These practices are consistent with widely adopted quality management principles. For example, the International Organization for Standardization (ISO) emphasizes process control, documentation, and continual improvement in quality management systems. A common reference point is ISO 9001, which is frequently used as a quality-management framework across sectors. You can also consult additional guidance around risk-based thinking and documented control practices in other ISO management system standards.
Reliable sources to consult include:
It can be helpful to expand the “why” in practical terms: reliability is not only about manufacturing quality; it is also about quality governance. Code-based identification supports governance by enabling consistent cross-referencing across teams: procurement, engineering, QA, operations, field service, and compliance. When the code-to-document mapping is stable, different teams can share a common understanding of what the item is and what it is supposed to do.
Additionally, code-based systems support root-cause analysis. Suppose a batch of assemblies fails a test. If you have traceability tied to Pi9691133599 and corresponding umefra189 references (and you can associate them to lots), you can isolate whether the failure correlates with a particular supplier lot, revision state, or material batch. Without those connections, root-cause analysis becomes largely statistical and speculative.
For risk-based quality management, the ability to map identifiers to controlled requirements enables more precise risk decisions. You can decide what sampling plan to use, what incoming checks to apply, and how to manage nonconformances. Even if you have to adjust risk controls over time, the identifiers provide the backbone of that risk control structure.
Therefore, code-based identification is a tool for reliability engineering and quality management. It is not just an administrative convenience.
Pi9691133599 is best treated as an identifier that must be mapped to a specific technical specification, configuration, or document set. Meaning depends on the issuing organization’s documentation, revision system, and product context.
In practical terms, you usually won’t interpret the code by reading it. Instead, you interpret it by locating the supplier’s crosswalk documentation or revision-controlled datasheet index that explicitly ties Pi9691133599 to a drawing or approved configuration. If you cannot find that mapping, then the identifier’s meaning is not yet actionable for procurement or QA.
umefra189 is likewise best approached as a structured reference. It may correspond to a product variant, internal catalog entry, or a batch-related label. Verification should rely on the supplier’s spec mapping.
Often, two codes appear together because one identifies a product configuration and the other identifies a packaging/lot/traceability component or a subcomponent variant. Without supplier explanation, the relationship between the codes may be unknown. Treat both as required verification keys rather than interchangeable labels.
Request a spec pack and revision-controlled documentation that explicitly references Pi9691133599 and umefra189. Then align your quote line items with the documented identifiers and acceptance criteria.
To make this step more concrete, you can ask targeted questions:
In technical procurement, visual similarity is not sufficient. Codes like Pi9691133599 often represent configuration or revision differences. Accept only items verified against documented requirements.
“Looks like the same” can fail due to small-but-critical differences: material treatment, coating thickness, dimensional tolerances, electrical ratings, firmware settings, or compliance test outcomes. Visual checks can catch gross mismatches, but they cannot verify the documented truth that traceability systems are intended to guarantee.
At minimum, your supplier should provide evidence that links the identifier to production lots and inspection outcomes relevant to your acceptance plan—typically through certificates of conformity and inspection/traceability records.
Traceability evidence is more useful when it is structured. For example, a batch/lot traceability report should clearly show which physical identifiers were produced from which material lots and which inspection results correspond to which delivered quantities. If the supplier provides certificates in a way that requires manual interpretation, that increases operational risk (errors during incoming inspection, delays during audits, or inability to quickly respond to nonconformance investigations).
Prices commonly vary due to revision level, documentation scope, compliance evidence, lead time, and batch characteristics tied to the identifiers. Since you did not provide a specific price, use formal quotes and compare documentation terms rather than assuming a fixed cost.
Even when unit prices are similar, total cost can differ significantly if documentation deliverables and inspection scope are included or excluded. Therefore, compare not only the numbers but the documentation scope tied to Pi9691133599 and umefra189.
No explicit location keywords were provided beyond placeholder-style text. If your project involves a specific delivery region, align supplier documentation and shipping/handling constraints with local operational practices and internal QA expectations.
Delivery region matters mainly in areas like logistics lead times, import/export documentation, environmental storage conditions during transit, and any local compliance labeling requirements. Even though location-related information is not specified in the codes, you should align receiving and handling procedures with the realities of shipment conditions.
Do not accept substitutions solely on functional description. Require equivalency evidence showing how the replacement matches the specification set associated with Pi9691133599 and umefra189, including revision and traceability implications.
A robust substitution acceptance process usually requires: documented equivalency mapping, any impact analysis on critical-to-quality characteristics, updated certificates, and confirmation that labeling and traceability still satisfy your acceptance and audit needs. If the substitution changes revision state or critical parameters, it should trigger formal approvals and potentially updated engineering documentation.
Organizations sometimes treat identifiers as administrative details. In practice, they are often the bridge between specification intent and actual delivered configuration. When that bridge breaks, risks include:
It’s useful to expand how each risk manifests in practice:
These risks are not hypothetical. Many organizations have faced “late discovery” failures, where paperwork suggests correctness but the delivered configuration differs because the identifier mapping was not validated. By implementing an identifier-centric verification approach early, you reduce the probability of such late failures and you shorten time-to-correction when issues occur.
As an expert advisor, I recommend adopting identifier-centric controls. When Pi9691133599 and umefra189 appear in procurement or technical documentation, treat them like “keys” that unlock specific verification steps. The simplest governance model is:
This is the foundation for predictable quality and smoother troubleshooting if an issue arises later.
To implement this model effectively, procurement teams can collaborate closely with engineering and QA through a shared checklist. A useful pattern is to define: (1) where the mapping is stored, (2) what fields must be present in supplier documentation, (3) what evidence is required for release into inventory, and (4) what happens when the supplier’s paperwork does not match the code in the purchase order.
For example, define internal acceptance gates:
This gate-based approach turns verification into a controlled workflow rather than a “best effort” practice. It also clarifies responsibilities. Procurement can ensure that the purchase order and RFQ language are correct. QA can ensure that inspection scope matches the risk. Engineering can ensure that interface and compatibility requirements are met. Together, they ensure that identifiers like Pi9691133599 and umefra189 are not just purchased—they are verified.
Another expert-level recommendation is to maintain an internal change log for any revision-related identifier updates. If a supplier changes the identifier mapping, or if Pi9691133599 is replaced by a new identifier for a revision update, you should record the change decision, approvals, and updated acceptance criteria. This prevents “silent drift,” where items change over time without clear organizational awareness.
Finally, remember that quality is a system property. Even if you have excellent internal processes, you rely on suppliers to provide accurate mapping and traceability evidence. Therefore, continuously evaluate supplier performance. If suppliers repeatedly mislabel lots, omit certificates, or provide mismatched revision documentation, that is a quality signal. Supplier scorecards and corrective action requests can motivate improvement and protect your operations over the long term.
When you see Pi9691133599 and umefra189 in supplier communications or technical materials, the responsible approach is to verify their mapping to the correct specification set and revision state. Then, ensure your procurement and acceptance process is aligned with traceability and quality documentation. Done correctly, this reduces mismatch risk and strengthens audit-readiness—turning coded identifiers into operational confidence.
In practice, this means you treat the codes as the starting point for a verification chain: code → documented mapping → quote line item alignment → delivery identity match → traceability evidence → incoming inspection and acceptance sign-off. Each link in the chain matters. If any link is weak, you risk hidden failure costs later. But if the chain is strong, you can manage quality predictably, troubleshoot effectively, and maintain compliance through evidence.
Ultimately, the identifier-centric approach reflects a broader maturity in technical procurement: you are not buying “something that seems similar.” You are buying a configuration with a documented identity, supported by traceability and evidence that your organization can verify. That is what turns a code like Pi9691133599 into actionable confidence across the entire lifecycle.



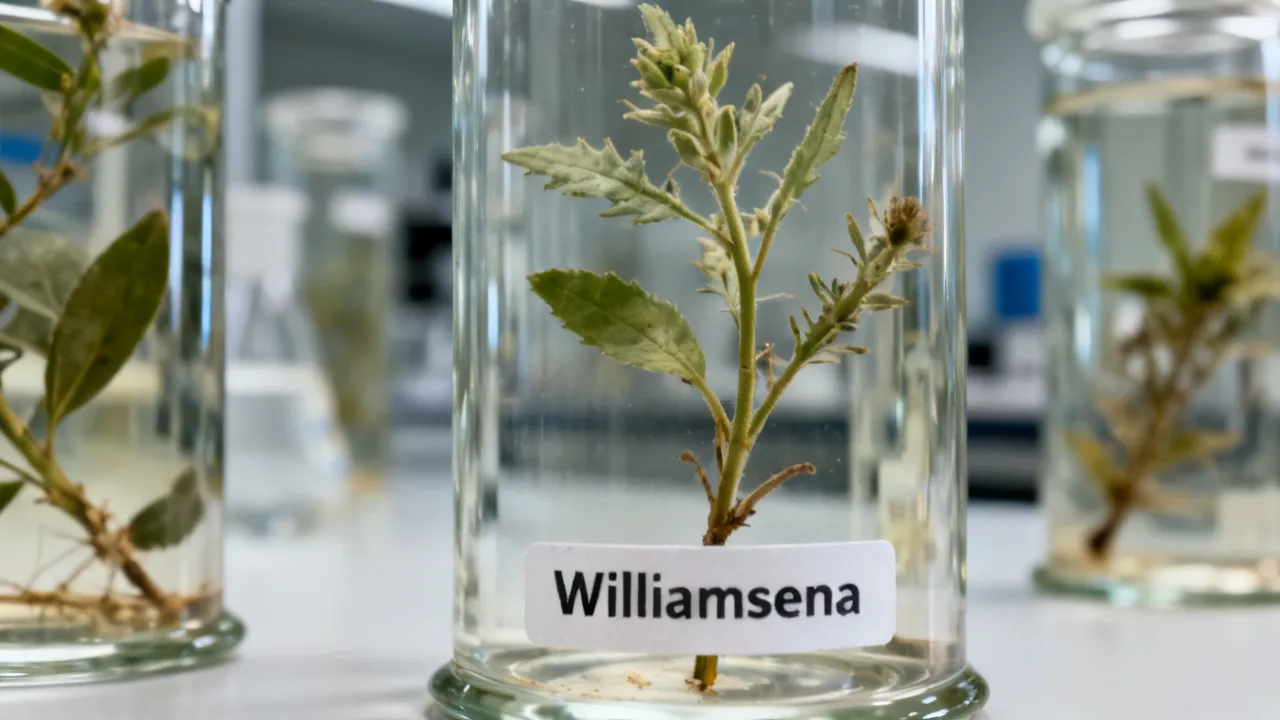
Williamsena can be understood as a botanical and research-oriented subject that matters for procurement, formulation, and quality control. This guide offers an objective background on the term “Williamsena,” outlines common sourcing considerations, and provides a decision framework for selecting reliable inputs. It also clarifies practical requirements and includes FAQs for informed, risk-aware selection.
This guide explains how to evaluate suppliers and manage sourcing decisions using the reference number 9691133599. It also provides objective background on supplier credibility, pricing transparency, and quality assurance, so you can compare options without relying on assumptions. The discussion is written for practical procurement planning, focusing on verifiable requirements, documentation, and risk control.
This guide explains how to interpret Pi9691133599, umefra189, and related identifiers for consistent procurement and safe deployment. It then provides objective background on why structured part or lot codes matter, how suppliers document specifications, and what due diligence looks like—without relying on unverifiable claims.
Esta guía explica cómo elegir y usar un Simulador Bb para practicar decisiones con datos simulados y evaluar escenarios sin improvisar. Luego, ofrece contexto objetivo sobre qué es un simulador de formación, para qué sirve en la industria y qué criterios técnicos suelen importar. El enfoque es práctico y orientado a análisis de riesgos.
This guide explains Pono as a practical concept tied to quality, integrity, and balanced decision-making. “Pono” is widely used in multiple contexts to describe something done well and in alignment with moral and functional standards. The article also examines how organizations and individuals can apply disciplined criteria when evaluating choices and building trust.
This guide explains how to evaluate Xivido in practical decision-making, from capability checks to supplier due diligence. Objectively, Xivido refers to a product or platform name used in the market with varying implementations and service scopes. The guide clarifies what to verify, how to compare offerings, and which requirements commonly matter to teams during procurement and rollout.

