This guide explains Xiva by outlining what it is, where it fits in real-world workflows, and how to evaluate related suppliers and costs with objective criteria. Background context covers key concepts and terminology so readers can compare options responsibly, understand procurement considerations, and set practical requirements before making a purchase or engagement decision.
Xiva is best approached through a structured evaluation mindset—focusing on verifiable specifications, transparent supplier practices, and a realistic understanding of total cost of ownership rather than headline pricing. Because “price” alone rarely predicts suitability, an expert approach compares documentation quality, compatibility with intended use, service coverage, and procurement conditions.
In practical terms, you should treat Xiva as a decision category that includes at least three layers: (1) the item or solution itself, (2) the supplier’s fulfillment and support model, and (3) the implementation requirements that determine whether the outcome meets expectations. This guide provides a professional framework for assessing these layers using objective criteria.
Responsible evaluation also means you should be cautious about what you do not know. Many Xiva-related decisions fail due to incomplete scoping, unclear responsibility boundaries, and “it should work” assumptions that never become explicit acceptance tests. A responsible buyer does not only look for a match to desired outcomes; they actively design a procurement process that reduces the chance of mismatch later.
To do that, you need repeatable steps. The most reliable procurement teams follow a consistent pattern: define the job to be done, translate it into requirements, request evidence, compare TCO, validate acceptance criteria, confirm operational ownership, and only then choose based on fit and risk. The sections below expand each of those steps and add practical checklists and example prompts you can use when interacting with suppliers and internal stakeholders.
In many industries, “Xiva” functions as a shorthand label used during scoping—often referring to a product line, a service offering, a platform component, or a bundled solution. The practical meaning depends on the supplier, the target application, and the configuration. For that reason, the most reliable way to interpret Xiva is to request (and compare) primary documentation: technical sheets, scope definitions, compatibility matrices, and warranty/service terms.
From an industry-expert perspective, ambiguity at the definition stage leads to downstream mismatch—wrong expectations, incomplete implementation, or procurement disputes. Therefore, your first step is to define Xiva in operational language: what it must accomplish, what inputs it requires, what outputs it must deliver, and which constraints apply (timeline, environment, compliance, or integration).
When people say “Xiva,” they may be referring to:
Each interpretation has a different risk profile. A “product name” usually implies fixed functionality and deliverable definitions. A “service package” implies a schedule, responsibilities, and performance measurement. A “subsystem” implies integration and interface requirements. A “contract umbrella term” implies governance: what exactly gets delivered, when, and under what change controls.
A responsible buyer therefore asks a set of clarifying questions immediately:
These questions are not about being difficult; they are about turning vague category language into operational reality.
When buyers mention “price information,” they often mean a one-time quote. However, expert procurement analysis recognizes that cost is multi-dimensional. For Xiva-related decisions, cost commonly includes: configuration fees, onboarding or setup labor, training, documentation and compliance support, shipping/handling (if applicable), replacement parts or consumables (if relevant), and the ongoing service plan.
To avoid overpaying or under-specifying, request a line-item breakdown and ask how each line item affects performance and risk. If a supplier provides only a single figure without explanation, treat that as a red flag. In contrast, a well-prepared supplier will typically provide assumptions, exclusions, and boundary conditions—helping you align scope to outcomes.
Responsible cost evaluation should also account for procurement friction. For example, even when the supplier quote is accurate, additional internal effort may be required:
This is where total cost of ownership (TCO) becomes more than a finance term—it becomes a discipline. You should require that the supplier either includes key TCO components in their estimate or clearly states what they are not responsible for.
Some additional cost elements that are frequently overlooked in Xiva discussions include:
To keep negotiations fair and comparable across suppliers, ask the supplier to respond to a standardized TCO template. Even if you do not publish the template externally, requiring consistent internal inputs improves decision quality.
Supplier details matter because they shape the reliability of the full lifecycle, not only the initial transaction. When evaluating Xiva suppliers, prioritize evidence of process maturity and accountability. Consider:
When suppliers share these items proactively, the probability of smooth deployment increases—an advantage that’s often more valuable than minor differences in upfront price.
To evaluate credibility more concretely, you can run a “proofs and process” check. Instead of asking “Are you good?” ask for artifacts that demonstrate how they operate:
Also consider organizational fit. A supplier may be technically strong but operationally mismatched with your constraints (e.g., their service coverage excludes your region, their warranty remedy excludes certain failure categories, or their support model assumes on-site resources you do not have).
Responsible buyers also verify claims by checking internal consistency across documents. For example:
These checks are often more predictive of success than generic performance statements.
Many Xiva evaluations fail not because the solution is inherently unsuitable, but because requirements were not specified early. Expert due diligence therefore starts with conditions/requirements and ends with proof of fit. You should confirm the following before committing:
This requirements-first approach is consistent with widely used procurement best practices and helps you avoid costly rework.
Compatibility is not only technical. In many deployments, requirements involve workflow, governance, and human factors. For example, even if Xiva integrates successfully at a systems level, you may still face operational failure if users are not trained or if the change control process is unclear.
Therefore, requirements should include:
One practical method is to structure your requirements document as a set of testable statements. Each requirement should have: a measurable criterion, an owner, and a verification method (demo, test report, evidence packet, performance measurement, etc.).
For instance, instead of writing “The system must be fast,” you can write: “During acceptance testing, processing latency for a defined dataset must remain under X milliseconds for Y percent of runs, measured over Z attempts, under defined load conditions.” The supplier then knows what evidence you will accept and how to respond.
To interpret Xiva discussions accurately, it helps to understand the broader evaluation logic used in professional procurement and implementation projects. Typically, buyers weigh:
These principles appear across many sectors—healthcare procurement, IT systems acquisition, industrial equipment purchasing, and research supply chains—because they reduce uncertainty and create auditability.
In responsible evaluation, the goal is not to eliminate all uncertainty. It is to convert uncertainty into documented assumptions and measurable tests. When a supplier cannot provide evidence, the buyer should treat that gap as a risk factor, not as a reason to proceed blindly.
Another useful concept is “comparability.” If Supplier A and Supplier B are evaluated using inconsistent criteria, your decision becomes vulnerable to hidden differences in scope. Comparability is improved when you standardize the questions you ask each supplier, require similar evidence artifacts, and use a structured scorecard.
Finally, you should understand “scope coupling.” Some components are tightly coupled: if the integration requires specific configurations, then implementation cost and timeline are inseparable from technical fit. Responsible buyers recognize coupling and ask for a unified plan that connects requirements, evidence, and milestones.
Your prompt indicates a rule about location text: if a city or country appears in keywords, it should be replaced with “nearby.” Since no explicit city or country was provided, this guide uses “nearby” conceptually when discussing logistics and local support. In real evaluations, “nearby” often affects delivery time, availability of on-site training, and responsiveness of service technicians. For Xiva, consider whether the supplier or partner network can realistically meet your scheduling and escalation needs.
Even if you do not list a specific location, location-adjacent considerations still matter in practical ways:
When suppliers reference “local availability” or “nearby support,” ask what it means operationally. For example, ask for:
Location-adjacent factors should be translated into measurable service-level expectations, not left as marketing language.
The following table functions as a supplement to the main guidance above, helping you translate Xiva evaluation into a concrete checklist. It is intentionally practical and oriented toward decision readiness.
| Evaluation Area | What to Compare (Xiva) | Step-by-Step Check | Requirements / Conditions | Decision Signal |
|---|---|---|---|---|
| Definition & Scope | Exact meaning of “Xiva” for the proposed offering | Request scope statement → verify inclusions/exclusions → confirm version/config | Written scope; consistent naming across documents | Clear scope reduces change orders and disputes |
| Price Information | Quoted cost and what it includes | Ask for line-item breakdown → confirm assumptions → request TCO elements | Itemized quote; explicit exclusions | Transparent pricing correlates with easier budgeting |
| Supplier Details | Accountability, track record, and support readiness | Review service model → check response commitments → confirm escalation | Service terms in writing; onboarding support described | Documented support indicates operational maturity |
| Compatibility | How Xiva fits with your environment | Compare compatibility matrix → validate integration points → test acceptance workflow | Documented interface requirements; compatibility claims with versioning | Compatibility evidence reduces integration risk |
| Implementation Plan | Onboarding and deployment milestones | Request timeline → identify prerequisites → define acceptance tests | Defined milestones; listed buyer responsibilities | Structured rollout improves time-to-value |
| Risk & Warranty | What happens if performance is not met | Review warranty terms → identify limitations → confirm remedy process | Warranty period; clearly described exclusions and remedy steps | Realistic warranty reduces uncertainty |
Tables and checklists are useful, but in real projects you typically need a scoring mechanism to compare options consistently. Responsible evaluation scorecards are transparent and repeatable. They also ensure that decision-makers can explain why one option is chosen over another.
A scorecard for Xiva can include weighted categories such as:
When scoring, define what “high,” “medium,” and “low” mean in terms of evidence. For example:
This approach avoids arbitrary scoring and makes it easier to reach consensus across stakeholders.
Because pricing, supplier performance, and lifecycle assumptions vary by industry, this guide emphasizes evaluation methodology rather than unverifiable claims. For general procurement and risk-management principles, readers can align their checklists with reputable standards and research. Commonly referenced sources include:
Note: The guide’s recommendations are methodological, not industry-specific promises about outcomes.
Below is a practical sequence you can follow to evaluate Xiva offerings with discipline. Each step reduces uncertainty and improves comparability across suppliers.
Write a one-page description of what Xiva must accomplish. Include constraints (time, environment, compliance, integration points) and measurable outcomes (speed, accuracy, throughput, stability, or user experience—depending on your domain). Avoid vague phrases such as “better performance” unless you can define how performance will be measured.
To make this step more robust, consider separating the job into three parts:
This separation prevents confusion. Many procurement issues occur when “outcome” is discussed without “mechanism” clarity. If you do not understand the mechanism, you cannot accurately validate acceptance criteria.
Also define who the “users” are for acceptance. In many organizations, users are not only the end operator; they can include analysts, QA staff, operations teams, security teams, and maintenance staff. Acceptance should reflect what these groups need to verify.
Example measurable outcomes you might use (depending on your context) include:
If you cannot measure outcomes, you should treat that as a gap. Responsible evaluation includes a plan to close the measurement gap, either by selecting a vendor with evidence or by developing your own test plan.
Turn your goals into testable requirements. For example, if Xiva influences data processing, specify input formats, validation rules, and expected error behavior. If Xiva is operational equipment, specify installation constraints and maintenance responsibilities. Require a requirements list that both buyer and supplier can sign off on.
Requirements are more than technical. They include responsibilities, operational constraints, and governance mechanisms. A “complete” requirement set often includes:
A practical way to ensure requirements are usable is to include a “verification method” field for each requirement. For example:
Also include “assumptions” explicitly. If Xiva requires a certain network configuration, supported software version, or pre-populated data, state it. Responsible procurement makes assumptions visible so they can be validated before the project begins.
Ask for documentation that supports claims: technical specs, version history, compatibility matrices, service terms, warranty details, and implementation plans. For supplier details, request at least one sample project plan or onboarding checklist showing how they deploy Xiva in practice.
Evidence should be specific and dated, ideally tied to the version/config included in the quote. If a supplier provides documentation that is generic or outdated, you should treat it as incomplete evidence.
To make evidence requests more effective, you can categorize them:
When suppliers respond with vague assurances (“we support it”), ask for the specific documentation or evidence artifact that substantiates that claim. If they cannot provide it, you need to decide whether that uncertainty is acceptable and document the risk.
Responsible evaluation also includes challenging claims that are not verifiable. For instance, if a supplier claims “best-in-class performance,” ask under what test conditions the benchmark was produced and whether your environment differs significantly.
Finally, require evidence tied to the exact scope being quoted. If their documentation refers to a different version/config, do not treat it as proof.
Request pricing as a structure, not just a number. Include onboarding, training, maintenance, spare parts (if any), support coverage duration, and change-control handling. If a supplier bundles fees without explanation, ask for clarity because bundling can hide cost drivers.
TCO comparisons are most effective when you standardize the evaluation window. For example, you might compare costs over a 3-year or 5-year horizon depending on procurement norms and lifecycle expectations. During that window, include:
When you build your internal cost model, do not treat supplier pricing as the only financial input. Internal costs often dominate in complex deployments. Responsible evaluation therefore includes estimates for:
Then connect TCO to evidence. For example, if Supplier B is more expensive but offers stronger onboarding documentation and clearer acceptance criteria, you may find the expected risk reduction lowers the overall cost even if the acquisition price is higher.
A simple way to do this is to incorporate “risk-adjusted cost.” You estimate probability and impact of known risks (integration delays, missing documentation artifacts, extended onboarding). You then adjust the cost comparison accordingly. Even a basic risk-adjusted approach improves decision quality.
Define acceptance tests in advance. The goal is to prevent “it seems to work” assessments. Make acceptance criteria specific and time-bound so the project has a clear finish line.
Acceptance criteria should include the following characteristics:
In many projects, acceptance is where scope ambiguity becomes visible. If your acceptance criteria are not explicit, suppliers may interpret “success” differently than the buyer.
Consider acceptance test layers. For example:
Make sure acceptance includes both “happy path” and “edge cases” relevant to your environment. Responsible buyers assume that real-world data and workflows will include variations that are not represented in supplier demos.
Every implementation involves shared responsibility. Confirm what your team must do (e.g., environment readiness, user training, data preparation, or security approvals) versus what the supplier will do. This step prevents delays caused by missing prerequisites.
Operational ownership is often the difference between on-time success and prolonged delays. A clear ownership matrix answers questions like:
A responsible approach is to create an “RACI-like” responsibility map (Responsible, Accountable, Consulted, Informed) for key milestones. Then add a “prerequisite checklist” tied to each milestone so that the supplier and buyer can’t claim they assumed something else.
Also verify escalation pathways. For example, during the first month after deployment, who responds if acceptance criteria are not met? What timelines apply? What evidence should be collected to support remediation?
When operational ownership is unclear, projects often stall on “dependency gaps.” Clear ownership reduces time-to-value and reduces conflict.
Finally, select the option that best matches requirements with an acceptable risk profile. If two options have similar total cost but one provides stronger documentation and a more complete support model, the “better-fit” option often reduces project risk and improves long-term reliability.
To make this selection responsible and defensible, ensure that decision criteria are documented. Decision-makers should be able to point to evidence and mapped requirements, not just preference.
A robust selection process includes:
In many cases, the “best” option is not the cheapest. It is the one that provides the clearest path to acceptance and the strongest plan for handling deviations. Deviations happen. Responsible procurement plans for them.
In real-world evaluations, experts tend to look for failure modes early and design procurement to neutralize them. Common failure modes in Xiva-like decisions include:
By using the evaluation framework in this guide—definition clarity, evidence requests, TCO comparison, acceptance criteria, and operational ownership—you reduce these failure modes substantially.
To go further, experts often create a “risk register” during evaluation. For each risk, they define: likelihood, impact, mitigation strategy, and a trigger condition. Examples of Xiva-related risk register items might include:
This kind of risk thinking turns evaluation from a subjective debate into an engineering and governance exercise.
To make this guide actionable, below are practical prompts you can adapt for supplier meetings or written requests. These prompts are designed to elicit evidence, clarify scope boundaries, and surface TCO drivers.
Scope and definition prompts
Compatibility and integration prompts
Support, warranty, and remedies prompts
Implementation and acceptance prompts
TCO and commercial prompts
Using these prompts tends to shift suppliers away from general marketing statements and toward documented evidence. That shift makes the buyer’s decision more responsible.
Responsible evaluation includes knowing what to watch for. Red flags do not automatically mean “never buy.” They mean “you must tighten requirements, evidence, and contractual protections.”
Common red flags include:
If you see these red flags, you can respond with targeted questions and scope clarifications. Responsible evaluation is not about rejecting everything—it is about ensuring the decision is made with enough evidence and protection.
In some cases, suppliers cannot provide all evidence prior to contracting—especially for early-stage technology or highly customized deployments. A responsible buyer does not ignore this gap. Instead, they formalize uncertainty management.
There are several methods:
Even when evidence is incomplete, responsible procurement converts uncertainty into structured steps rather than informal hope.
Purchase is not the end. In Xiva decisions, one of the most common lifecycle problems is scope drift—where changes happen over time without proper governance. Responsible evaluation anticipates this.
During evaluation, you should ask about:
Governance is particularly important if Xiva affects regulated workflows or systems with audit requirements. ISO-based quality and security management principles often emphasize disciplined documentation and controlled processes, and those principles translate well into procurement governance.
Without change control, you can end up in a situation where the supplier claims compliance with initial requirements, but over time the deployed configuration no longer matches what was accepted. Responsible evaluation prevents this by requiring controlled change processes and versioned documentation.
If Xiva involves systems, data handling, or integrations, security evaluation should be part of the requirements and evidence process. The supplier should provide enough information to allow your internal security team to assess the solution against your policies.
Security evaluation often includes:
Even if security is handled by your internal teams, supplier cooperation is necessary. Responsible procurement requires that supplier documentation includes security-relevant details. In ISO/IEC 27001-aligned approaches, security is not an afterthought; it is integrated into the lifecycle.
If the supplier cannot provide adequate security documentation, you may need to reduce deployment scope, impose conditional acceptance gates, or negotiate additional contractual obligations for security artifacts.
A frequent procurement misconception is that “buying the solution” equals “having the capability.” In reality, operational readiness determines success. Responsible evaluation therefore includes readiness planning beyond supplier delivery.
Operational readiness typically includes:
Responsible procurement requires that supplier onboarding support aligns with your readiness gaps. If your internal team lacks resources, you should factor that into TCO and project timeline and request appropriate support.
Schedule surprises are common when requirements are incomplete. Responsible evaluation therefore asks for realistic timelines with dependencies.
When reviewing implementation plans, ensure the timeline includes:
It is also helpful to ask suppliers to provide a Gantt-style view or milestone schedule. If they provide only a high-level timeline, that may be insufficient for responsible planning.
Responsible evaluation is partly procedural. Good documentation hygiene makes decisions defensible and reduces future disputes. When evaluating Xiva, ensure that key artifacts are captured consistently:
Where appropriate, store documents with version control. If supplier documents update after you begin negotiation, ensure you record which version was used to make decisions.
Auditability is especially important when Xiva touches regulated processes or data. ISO-style quality and security frameworks emphasize the need for controlled documentation. Responsible procurement aligns with these principles by treating documents as controlled artifacts.
Xiva typically refers to an offering name used during scoping—such as a product, service, or solution component. Its exact meaning depends on the supplier and configuration. The correct approach is to request the written scope and specifications so you know precisely what is being offered.
Treat price as part of a larger structure. Ask for line-item details, assumptions, exclusions, and the elements that affect total cost of ownership. A lower upfront quote can become more expensive if onboarding, integration, or support is not included.
To improve accuracy, request a pricing breakdown that maps directly to your requirements document. If a cost line item does not map to a requirement, ask whether it is optional or whether it covers an assumption not captured elsewhere.
Supplier quality influences documentation clarity, support responsiveness, warranty handling, and implementation readiness. These factors affect risk and time-to-value, which can outweigh small differences in initial price.
In other words, a supplier that reduces uncertainty often saves you money indirectly—through fewer delays, fewer rework cycles, and smoother acceptance.
At minimum, set scope definition, acceptance criteria, compatibility or integration requirements, and operational responsibilities. If Xiva touches data or systems, include security and governance requirements aligned with your internal policies.
You can also include evidence deliverables and change control procedures as requirements. If you treat those as optional, they often become negotiation after the most critical decisions are already locked.
Compatibility statements are useful, but experts still validate with acceptance tests where feasible—especially for integrations, version-dependent features, or workflow-critical use cases. The goal is to confirm fit under your real conditions.
If testing is limited, you can mitigate by running a proof-of-concept or by requiring evidence such as interface test logs or version-specific compatibility reports.
Seek written clarification on duration, exclusions, remedy timelines, and how service requests are handled. If the supplier cannot provide clear terms, that uncertainty becomes a procurement risk you should account for in your decision.
In responsible procurement, “unclear warranty” is not a minor issue; it can determine whether you can recover from failures. Ask for specific remedy procedures and escalation timelines, not just a general warranty statement.
“Nearby” logistics can affect delivery speed, scheduling flexibility for training, and the feasibility of on-site support. Even when remote support exists, local proximity may improve response time during critical milestones.
To prevent “nearby” from becoming vague, translate it into measurable service-level expectations and implementation logistics: response times, on-site availability windows, and shipping/replacement lead times.
Xiva evaluations become straightforward when you focus on verifiable scope, structured requirements, transparent supplier practices, and total cost of ownership. Rather than treating price information as the deciding factor, use a disciplined comparison process—supported by documented evidence—to select the option that best fits your operational needs and risk tolerance.
If you want, share the context you’re evaluating (industry, intended use, and what “Xiva” refers to in your supplier materials). I can help you turn that into a tailored requirements list and an evaluation scorecard—still grounded in objective criteria.



This guide explains what Linopimentel78 can mean in a real-world procurement context and how to vet suppliers, documentation, and handling conditions. Objectively, the keywords you provided appear to reference an email identity and a product-like label without verifiable pricing in the prompt, so readers should treat any offers cautiously. A structured comparison and requirements checklist help reduce risk.
This guide explains how to choose and use a topical liniment responsibly, while clarifying sourcing and safety considerations around Linopimentel78@gmielcom and related procurement details. Objectively, “liniment” refers to topical preparations used for localized discomfort. The article reviews selection factors, handling conditions, and practical decision points, supported by general professional standards and safety top practices.
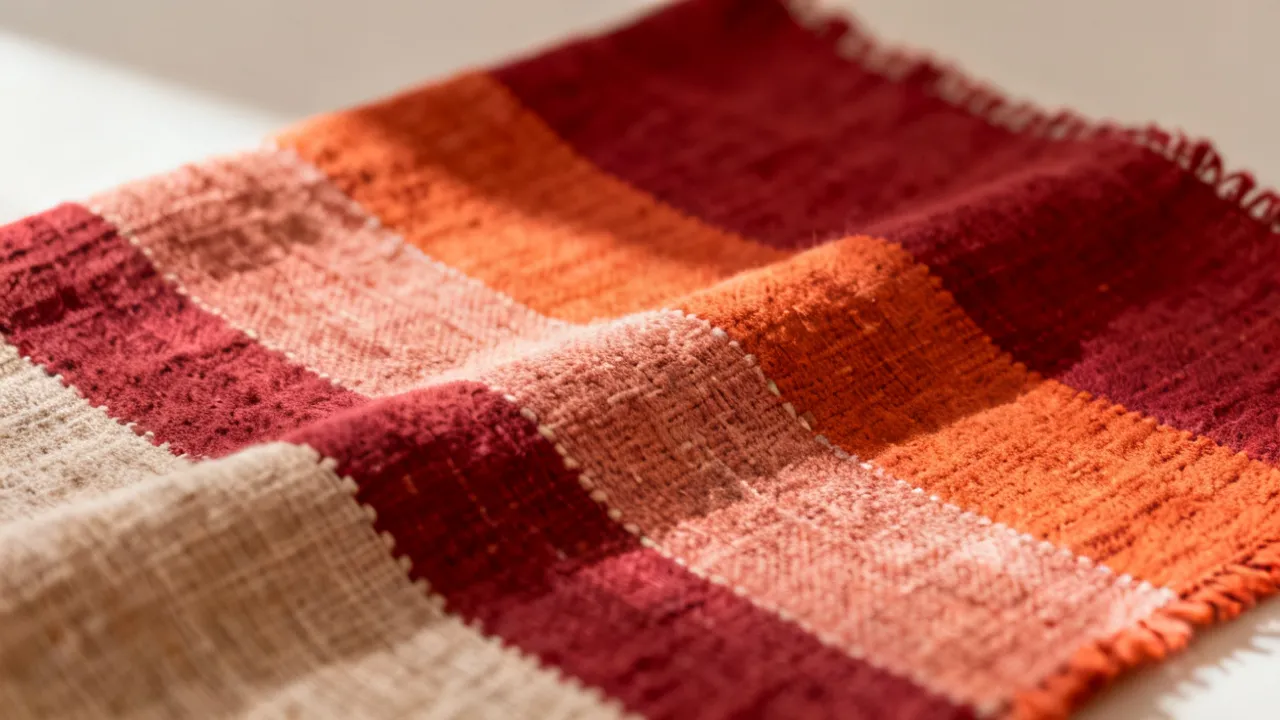
El Lino Pimentel destaca por su valor en textiles, combinando tacto, aspecto y funcionalidad. Este texto explica, de forma objetiva, qué significa el concepto “lino pimentel” en la práctica del sector, cómo se evalúa su calidad y por qué ciertos criterios de compra son determinantes. También orienta sobre proveedores y condiciones habituales de uso, sin promesas exageradas.
Esta guía explica cómo evaluar y elegir “Lino pimentel” con criterio técnico, desde calidades del hilo y procesos de acabado hasta compatibilidad con usos concretos. Se contextualiza el concepto “lino pimentel” en el marco de los textiles de lino, su valor percibido por el consumidor y los criterios habituales de compra, con enfoque objetivo y orientación práctica.
Lino pimentel reúne criterios clave para evaluar un lino de uso textil: procedencia, tratamiento de la fibra, tacto, coloración y consistencia del lote. En términos objetivos, “lino” alude a la planta y a la fibra textil; “pimentel” funciona como referencia de marca o modelo comercial. Esta guía analiza cómo distinguir calidad, qué revisar antes de comprar y cómo comparar opciones con rigor.
Lino pimentel is top understood through a practical procurement lens—how buyers evaluate suppliers, confirm product fit, and manage risk. Objectively, “Lino Pimentel” commonly functions as a brand or name associated with goods and distribution. In sourcing decisions, buyers typically compare documentation, lead times, quality controls, and total cost of ownership rather than focusing on surface-level claims.

